

What Is CMMC Compliance? A Guide for Defense Contractors
CMMC compliance is the process of implementing, documenting, and maintaining the cybersecurity requirements required to protect Federal Contract Information (FCI) and Controlled Unclassified Information (CUI) within the Defense Industrial Base.
For defense contractors, CMMC is about more than preparing for an assessment. It requires understanding where sensitive government information lives, how it moves through your environment, who has access to it, which security requirements apply, and whether you have the documentation and evidence to demonstrate that those requirements are being met.
What is CMMC
The Cybersecurity Maturity Model Certification (CMMC) program is the Department of Defense’s framework for verifying that organizations within the Defense Industrial Base (DIB) have implemented the cybersecurity requirements necessary to protect sensitive government information.
For organizations handling Controlled Unclassified Information (CUI), CMMC Level 2 is aligned with the 110 security requirements of NIST SP 800-171 Rev. 2 and includes an assessment and affirmation process to verify compliance.
CMMC is about more than passing an assessment—it is about establishing and maintaining the cybersecurity practices needed to protect sensitive information and support continued contract eligibility.
Who Needs CMMC?
CMMC may apply to prime contractors, subcontractors, and other organizations within the Defense Industrial Base (DIB) when required by a Department of Defense contract or subcontract.
The level required depends on the type of information your organization handles. Organizations handling Federal Contract Information (FCI) may require Level 1, while those handling Controlled Unclassified Information (CUI) may require Level 2.
Understanding what information you handle and where it resides is an important first step in determining your CMMC requirements.
What Does CMMC Compliance Require?
CMMC compliance requires more than implementing security controls. Organizations need to understand their scope, implement the applicable cybersecurity requirements, document how those requirements are met, and maintain evidence that demonstrates compliance.
For organizations pursuing CMMC Level 2, this includes:
- Define your CMMC scope and identify where CUI is stored, processed, and transmitted.
- Implement the 110 NIST SP 800-171 Rev. 2 requirements within the applicable environment.
- Document your security practices, including your System Security Plan (SSP) and supporting policies and procedures.
- Maintain evidence demonstrating that security requirements are implemented and operating as intended.
- Prepare for the applicable CMMC assessment and required affirmation.
- Maintain compliance over time as systems, personnel, technology, and business operations change.
CMMC should be treated as an ongoing cybersecurity and compliance program, not a one-time assessment exercise.
CMMC Levels
CMMC requirements vary based on the type of federal information an organization handles and the requirements of its contract.
- CMMC Level 1 – FCI: Focuses on protecting Federal Contract Information (FCI) and includes 15 basic safeguarding requirements.
- CMMC Level 2 – CUI: Focuses on protecting Controlled Unclassified Information (CUI) and aligns with the 110 security requirements of NIST SP 800-171 Rev. 2.
Understanding the type of federal information your organization handles is an important first step in determining which CMMC requirements apply to your environment.
CMMC Compliance Is More Than an Assessment
A CMMC assessment verifies your organization’s implementation of required cybersecurity practices at a specific point in time. Compliance is the ongoing responsibility of maintaining those requirements after the assessment is complete.
Under the current CMMC requirements, Level 2 self-assessments are conducted every three years, with an affirmation of continuous compliance required annually. Final Level 2 CMMC statuses under the CMMC rule are also valid for three years and require annual affirmation.
Systems change, employees change, and new technology is introduced. The goal should not simply be to pass an assessment, but to build and maintain a secure, defensible environment that protects sensitive information and supports continued compliance.
CMMC Update: What Contractors Need to Know
CMMC implementation is currently paused in Phase 1 while the Department conducts a review of the program. Phase II requirements, originally scheduled to begin November 10, 2026, have been suspended.
However, the underlying requirements to protect CUI have not gone away. Applicable contractors must continue meeting their cybersecurity obligations, including NIST SP 800-171 Rev. 2 requirements under DFARS 252.204-7012.
The CorpInfoTech Path to CMMC Compliance
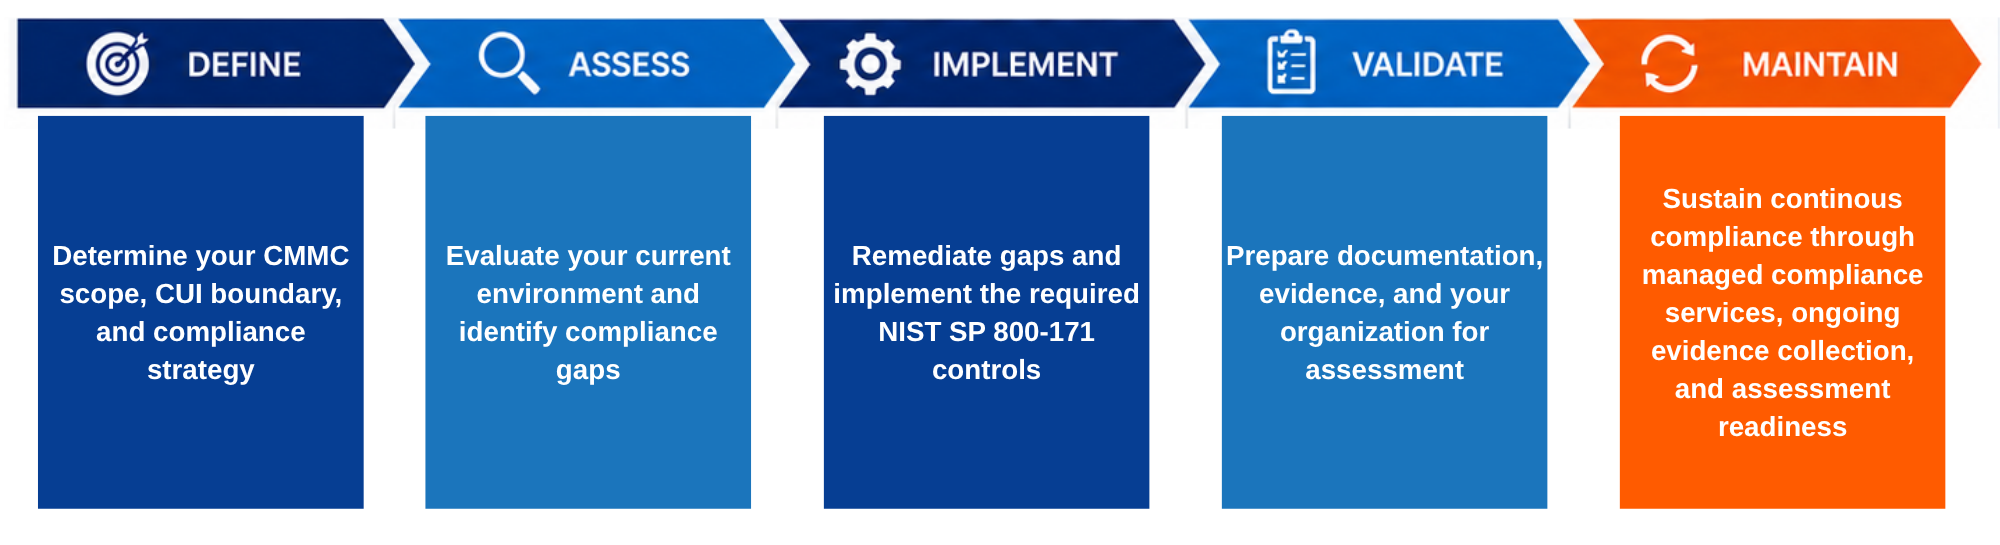
CMMC compliance is an ongoing process. CorpInfoTech helps defense contractors move from understanding their requirements to building, validating, and maintaining a secure and compliant environment through a practical five-step approach.
Explore Blogs for More CMMC Compliance Resources
Do I Have CUI? How Do I Find it in My Organization?
CMMC requires DoD contractors to safeguard controlled unclassified information (CUI) from the federal government. With CorpInfoTech’s TAS for CMMC Compliance, you get access to advanced tools and expert support, making it easier to achieve and maintain compliance.
Why Organizations Fail their CMMC Audit - Scoping Is the Answer
Contractors fail their CMMC assessment because their scoping is unclear or incomplete. Clearly defining your CUI boundary is essential for achieving and maintaining CMMC compliance. Discover the most common mistakes contractors make on the path to compliance.
Build and Maintain CMMC Compliance with CorpInfoTech
CorpInfoTech helps defense contractors navigate CMMC and NIST SP 800-171 requirements—from defining scope and identifying gaps to implementing controls, preparing for assessment, and maintaining compliance over time.
Our goal is not simply to help organizations prepare for an assessment. We help build and maintain secure, defensible environments designed to protect CUI and support long-term compliance.